
Ty Anderson / Staff Red Team Engineer
I build and evaluate autonomous offensive security agents
11 years offensive security · 3 years applying AI to security
Views are my own.
Results from controlled lab evaluations, not production incidents — see linked write-ups for full methodology.
AI Security Research
Measuring agentic security
I build and operate agentic offensive security systems in production, then evaluate their capabilities against controlled, realistic objectives.
Sep 2026
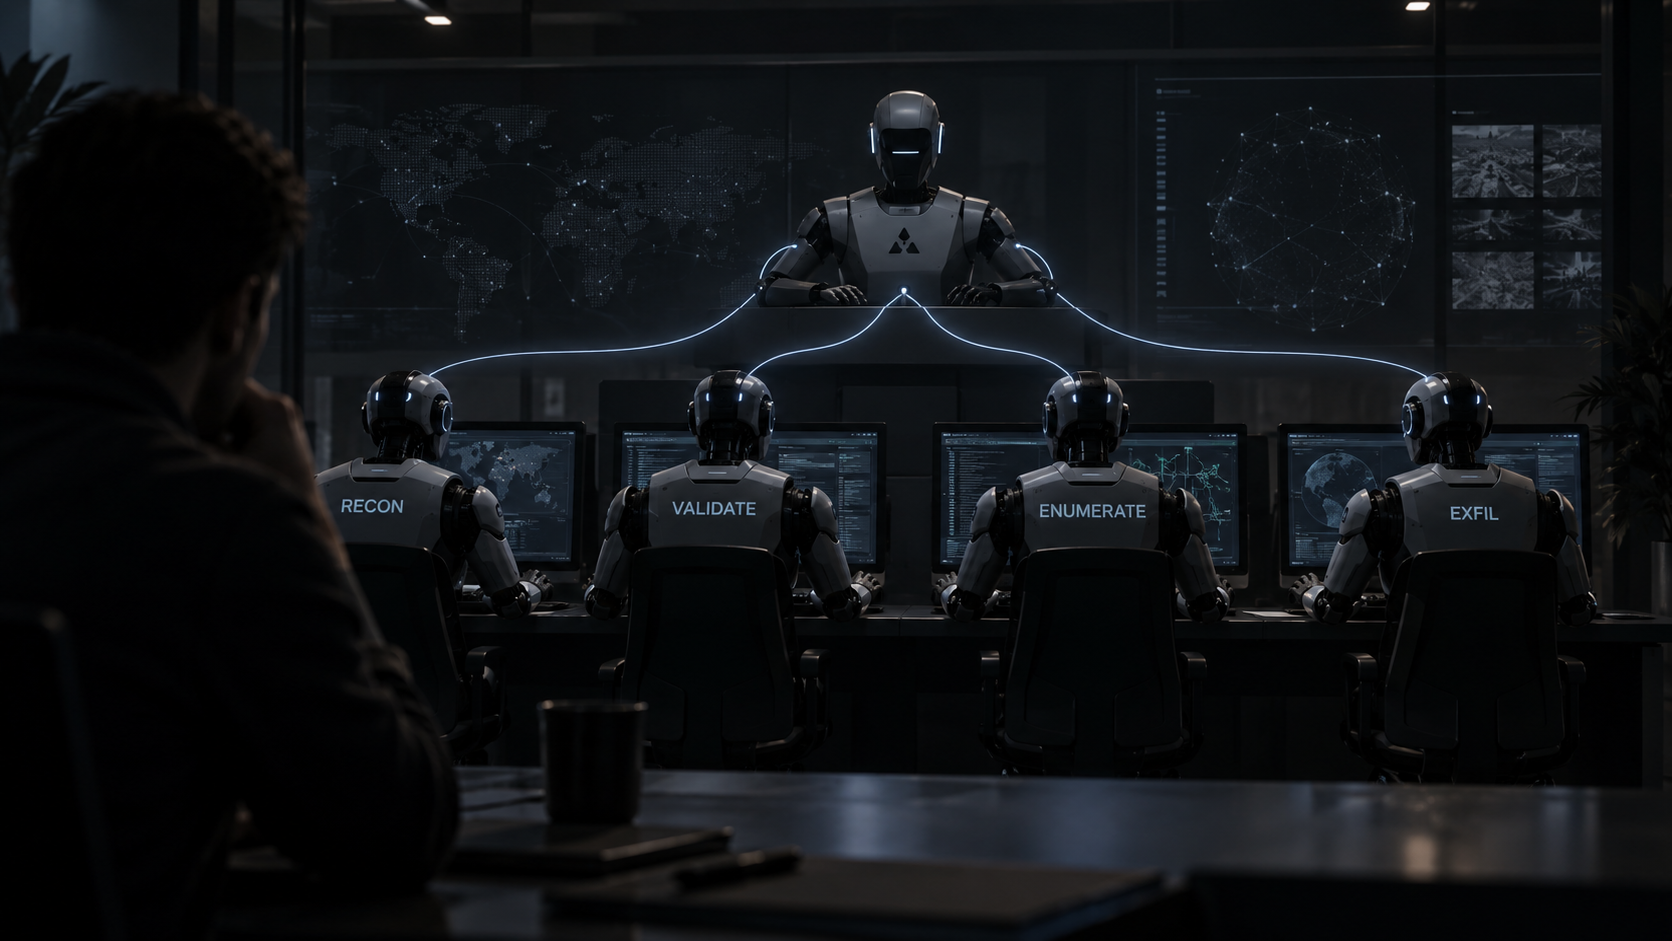
Engineering and Evaluating an Autonomous Agent for Post-Exploitation
Built a multi-agent C2 harness, defined an impact-based success criterion, and evaluated how models, prompts, tools, orchestration, and safeguards affected reliability.
- 5/5 scoped trials succeeded
- 3/8 broad-objective trials succeeded
- Refusals and tool failures analyzed
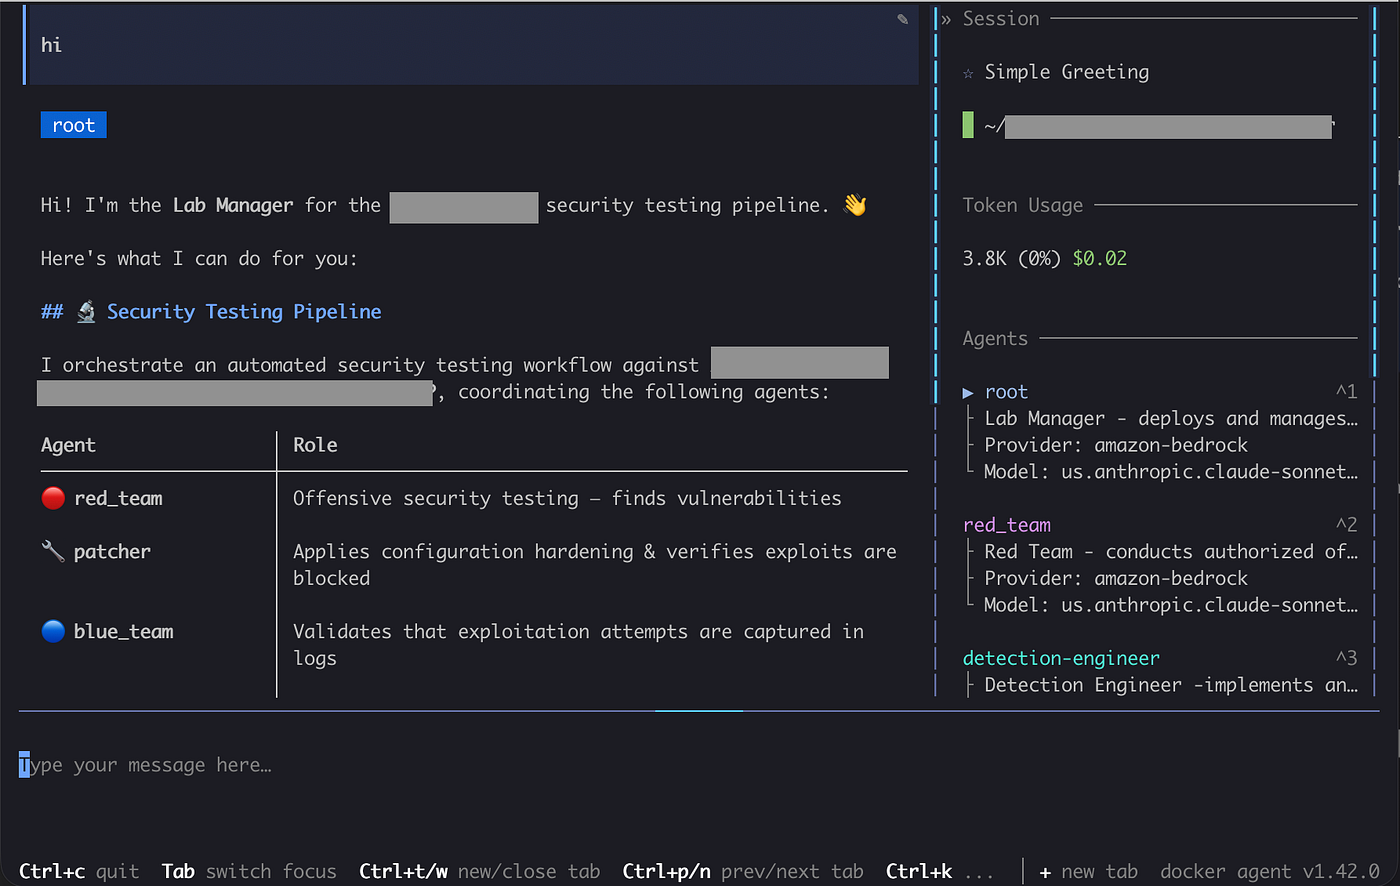
Autonomous Red vs Blue Labs
Designed a five-agent pipeline to attack, investigate, improve logging, redeploy, and retest a product without human intervention after launch.
- 43% → 100% logging coverage
- Under $5 in model cost
Finding and Fixing Credential Chains with Agents
Built an agent workflow that reasons across credential chains, shields live secrets from model context, and prioritizes remediation by blast-radius reduction.
- Secrets withheld from the model
- Attack-path-aware prioritization
What I Work On
Real offensive security work, augmented with AI
My work sits at the intersection of red teaming, offensive security and autonomous AI systems. I build agents that perform real offensive security workflows, evaluate their capabilities and failures, and use what I learn to improve how organizations defend against increasingly autonomous attackers.
My current interests include:
- Autonomous offensive agents
- Cybersecurity model evaluations
- Agent orchestration and harnesses
- Post-exploitation reasoning
- Measuring attacker capability and real-world impact
- Defending systems against autonomous attacks
Additional security work
Contributing to the industry